CLA News / Africa Legal Forum Session 5A: Data, Cybersecurity and Liability: Managing Risk in Digital Economies

As Africa’s digital economy accelerates, stronger data protection, clearer accountability and effective enforcement are essential to building trust and tackling emerging cyber risks.
Digital trade creates enormous opportunities for Africa, but it also exposes individuals, businesses and institutions to growing risks. From cross-border data transfers and artificial intelligence to cybercrime, SIM-swap fraud and harmful online content, a central question remains: when something goes wrong, who is accountable?
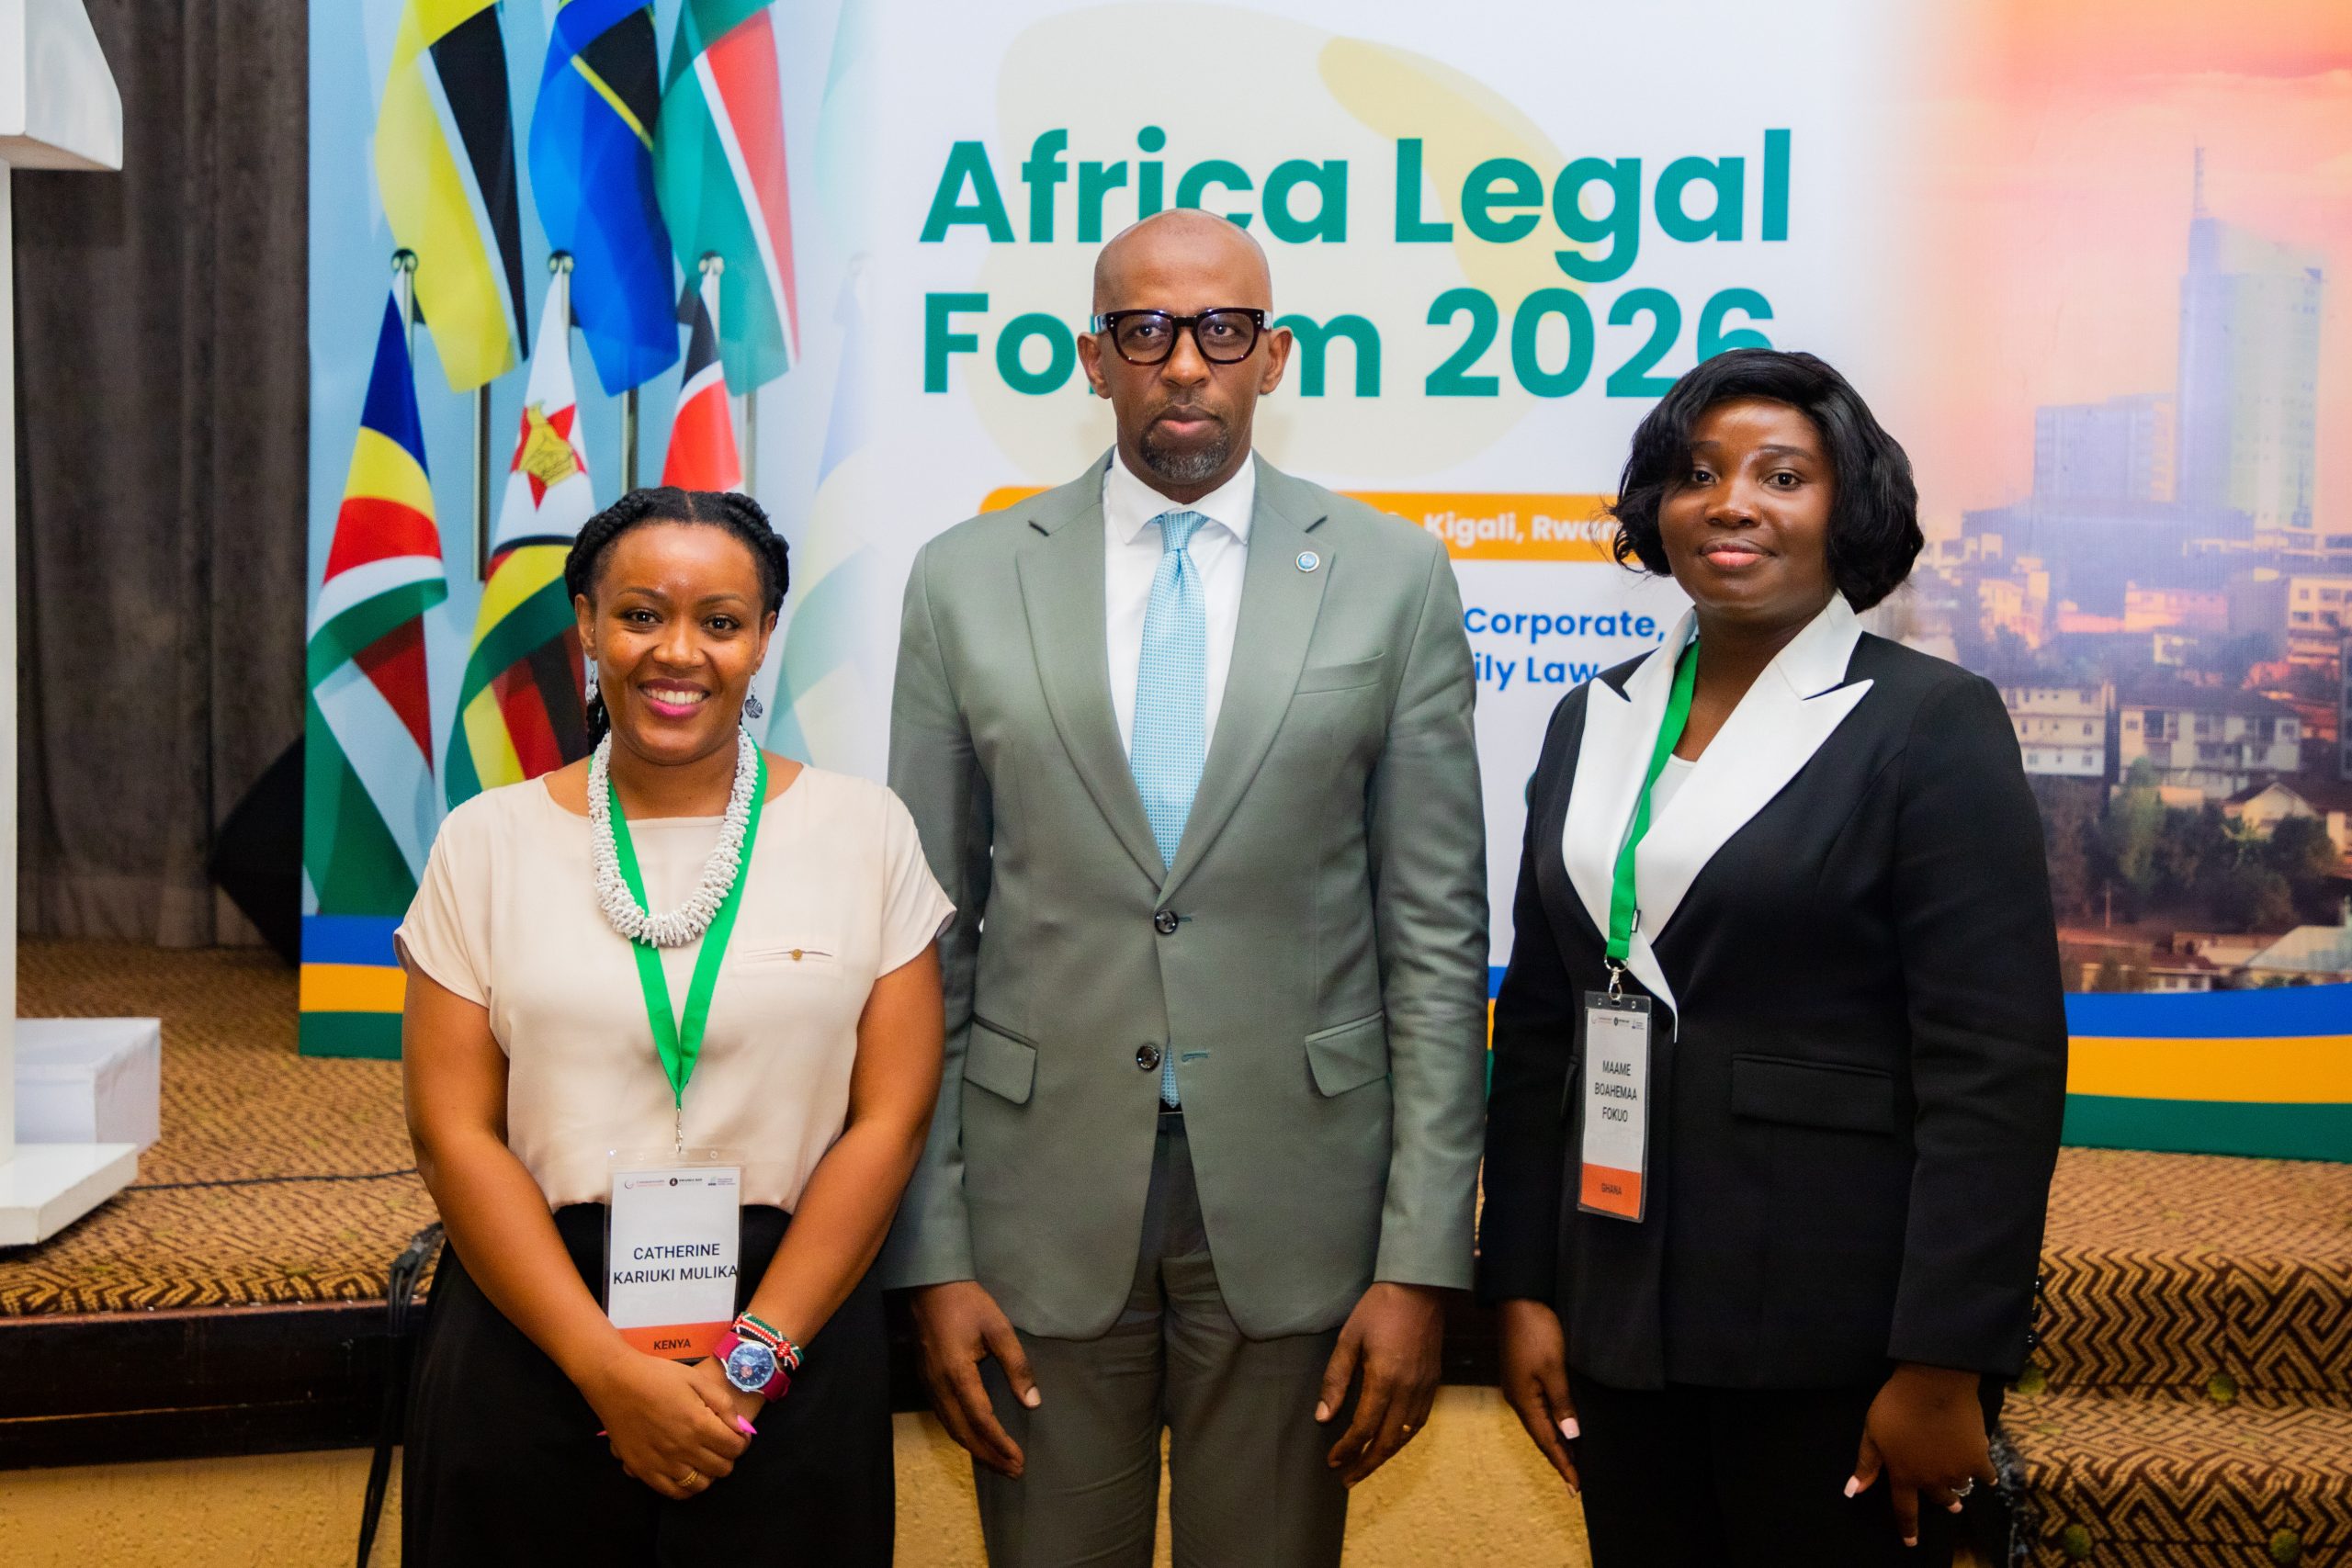
At Session 5A of the Africa Legal Forum, Data, Cybersecurity and Liability: Managing Risk in Digital Economies, chair Catherine Kariuki led a discussion with Dr Thierry Murangira and Maame Boahemaa on the legal frameworks, regulatory challenges and professional responsibilities shaping Africa’s digital future.
Building a coherent African data protection framework
As law firms and businesses increasingly handle vast amounts of personal information, legal practitioners must recognise their responsibilities as data controllers and protect the information entrusted to them.
The introduction of the EU’s General Data Protection Regulation (GDPR) in 2018 helped accelerate global attention to data protection, influencing how organisations approach international trade and the handling of personal information. Across Africa, a growing number of jurisdictions have since introduced their own data protection laws.
Yet the landscape remains fragmented. Some countries are still developing legislation, while others have laws but lack adequately resourced authorities to enforce them. Effective data protection requires more than legislation on paper: regulators need the institutional capacity, funding and technical expertise to investigate breaches and hold organisations accountable.
Kenya offers an example of increasingly active enforcement. Since its data protection regulator was established in 2019, the country has taken significant steps to strengthen oversight, including issuing compensation notices in cases involving personal data.
The broader challenge is to move beyond a patchwork of national rules towards greater consistency. Practitioners operating across jurisdictions should not have to navigate entirely different compliance systems at every border.
Regional harmonisation could provide a practical way forward. Drawing comparisons with developments in competition regulation, the discussion explored the potential for more coordinated oversight across East Africa, creating a bridge towards a more coherent continental framework.
The African Union’s Malabo Convention on Cyber Security and Personal Data Protection, adopted in 2014, and its 2022 Data Policy Framework provide important foundations for this ambition. The wider objective is to facilitate trusted cross-border data flows that support digital trade while safeguarding individuals’ rights.
Cross-border data flows demand cross-border accountability
Maame Boahemaa examined cross-border data governance and the accountability gaps that emerge when personal information moves between countries.
Data protection cannot stop at national borders. Information shared through social media, digital services and commercial platforms may be stored, processed or used in jurisdictions far removed from the individuals concerned. Establishing which laws apply, who controls the information and which authority can act becomes increasingly complex.
Accountability is therefore central to effective data governance. Clear responsibilities, proportionate sanctions and cooperation between regulators are needed to ensure that organisations cannot evade scrutiny simply because data crosses a border.
The challenge is not only to enable digital trade, but to ensure that the movement of information is accompanied by enforceable safeguards.
Cybersecurity, AI and the question of liability
Dr Thierry Murangira brought an investigative perspective to the discussion, highlighting how digital life has created new opportunities for crime while complicating the task of identifying those responsible.
Individuals increasingly live a dual existence: one in the physical world and another online. Personal information shared through everyday digital activity can be analysed, exploited or used against its owner. Cybercriminals take advantage of this exposure, while weaknesses in verification systems and inadequate cybersecurity can leave consumers vulnerable.
SIM-swap fraud illustrates the problem. Criminals can exploit weaknesses in SIM-card replacement procedures to take control of a victim’s telephone number, potentially gaining access to accounts linked to mobile banking and financial services. When losses occur, responsibility may be disputed between banks, telecommunications providers and fintech businesses, leaving victims struggling to obtain redress.
Clear legal responsibility matters as much as technical protection. Investigators and lawyers must establish what happened, identify the relevant failures and determine who can properly be held liable.
Artificial intelligence adds another layer of complexity. AI-generated images and videos can impersonate individuals, fabricate events or circulate damaging allegations. Distinguishing authentic material from manipulated content requires sophisticated investigative tools, while criminal proceedings raise difficult questions about evidence and admissibility.
The session also challenged the assumption that responsibility rests solely with the individual who publishes harmful material online. Platforms can be used to facilitate cyberbullying, sextortion, scams and other forms of abuse. Determining when a platform should bear responsibility, alongside the person committing the offence, requires clearer legal standards and careful consideration of the duties owed by digital service providers.
As Dr Murangira emphasised, effective accountability depends on establishing the facts, identifying the responsible parties and ensuring that legal frameworks can respond to the realities of digital offending.
The role of lawyers: defending the public interest
The discussion highlighted a persistent gap between the speed of technological change and the development and enforcement of laws capable of addressing its risks.
Cybersecurity failures, data protection breaches and digital fraud do not always fit neatly within national legal frameworks. Differences in criminal laws, regulatory powers and enforcement capacity can allow responsibility to be disputed or cases to stall.
Lawyers have an essential role in closing that gap. Beyond advising businesses on compliance, they can challenge inadequate safeguards, support victims seeking redress and pursue public interest litigation where regulatory or legislative shortcomings leave consumers exposed.
This requires legal practitioners to understand not only data protection legislation, but also cybersecurity, digital evidence, platform governance and the allocation of civil and criminal liability.
Trust is the foundation of the digital economy
The message from Session 5A was clear: Africa’s digital economy cannot realise its full potential without public trust.
That means building effective data protection regimes, strengthening cybersecurity, resourcing regulatory authorities and establishing clear lines of accountability for individuals, businesses and digital platforms. It also means improving cross-border cooperation so that legal protections remain meaningful when data and digital services move between jurisdictions.
Technology may cross borders in seconds. Accountability must be able to follow.
For Africa’s legal profession, the challenge is to help shape a digital economy that is innovative and commercially dynamic, while protecting rights, securing personal information and ensuring that those responsible for harm can be held to account.